|
|
|
|
|
|
Hi Kinbay
SKB is requesting an update on that security vulnerability.
Please let me know if there is any update.
Thank you
YK.Jung |
|
|
|
Hi YK,
The security vulnerability occurs after the below patch.
https://cs.android.com/android/_/android/kernel/common/+/92f1655aa2b2294d0b49925f3b875a634bd3b59e
But we have not updated the kernel for a long time before this.
So we suggest ignore it for now
BR,
Kinbay |
|
|
|
Hi Kinbay
Could you check below site ?
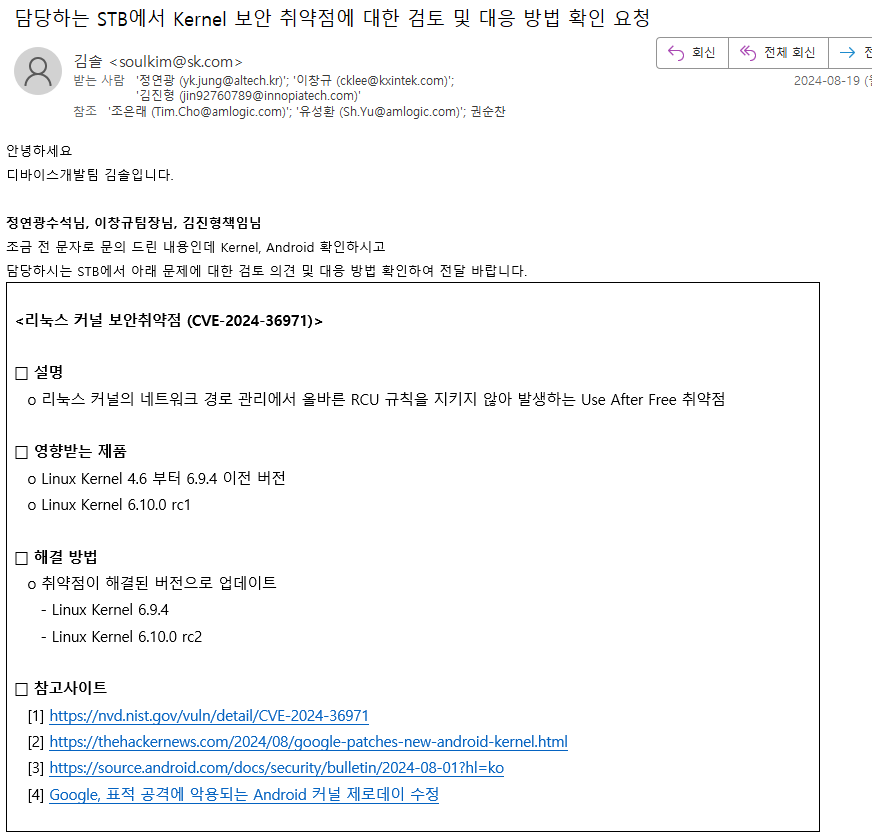
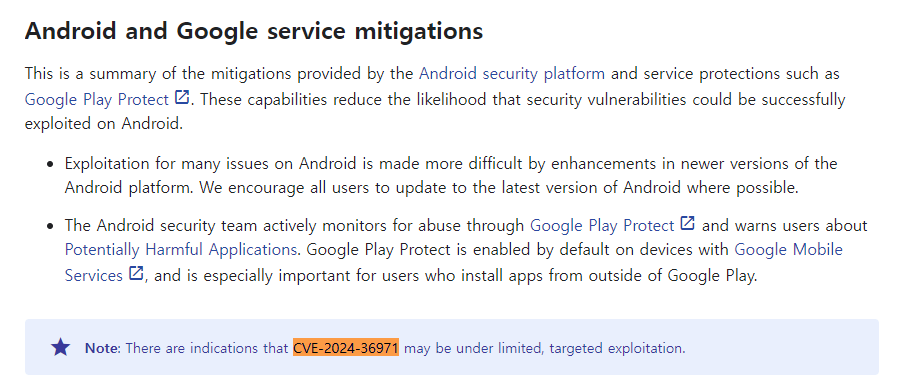
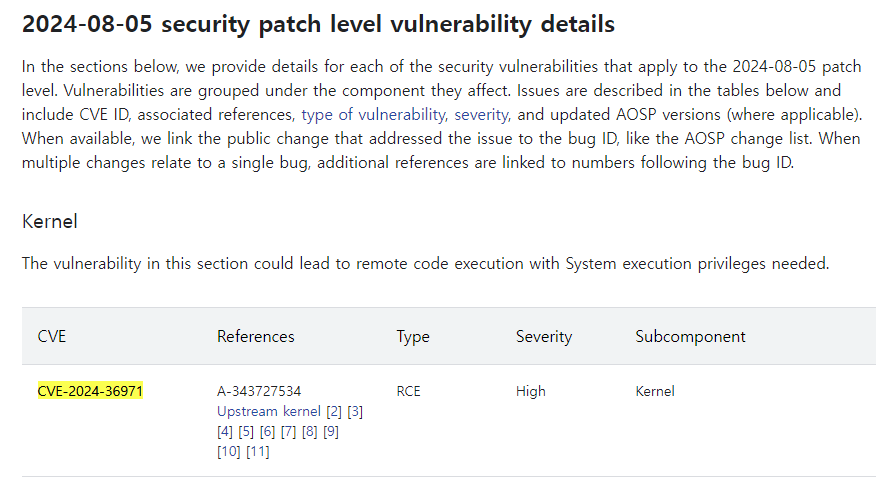
https://source.android.com/docs/security/bulletin/2024-08-01
If we apply Security patch 2024-08, will this security vulnerability be resolved?
Thank you
YK.Jung |
|
|
|
Hi YK,
We found the two patches to fix up.
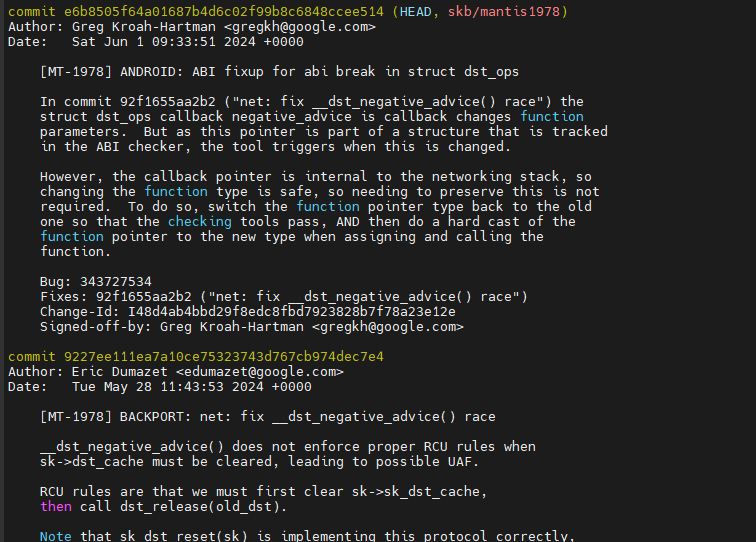
The security vulnerability occurs after 0001-BACKPORT-net-fix-__dst_negative_advice-race.patch
Then fix by the 0002-ANDROID-ABI-fixup-for-abi-break-in-struct-dst_ops.patch.
But our source does not include the 0001-BACKPORT-net-fix-__dst_negative_advice-race.patch.
So we suggest ignoring it for now.
If we apply Security patch 2024-08, will this security vulnerability be resolved?
-> No, I checked the 2024-08 security patch does not include the fixup.
BR,
Kinbay |
|
|
|
0001-BACKPORT-net-fix-__dst_negative_advice-race.patch (6,991 bytes)
From 1688b4ce3ed9959e79a5e3a1e9be331184a1b65d Mon Sep 17 00:00:00 2001
From: Eric Dumazet <edumazet@google.com>
Date: Tue, 28 May 2024 11:43:53 +0000
Subject: [PATCH 1/2] BACKPORT: net: fix __dst_negative_advice() race

__dst_negative_advice() does not enforce proper RCU rules when
sk->dst_cache must be cleared, leading to possible UAF.

RCU rules are that we must first clear sk->sk_dst_cache,
then call dst_release(old_dst).

Note that sk_dst_reset(sk) is implementing this protocol correctly,
while __dst_negative_advice() uses the wrong order.

Given that ip6_negative_advice() has special logic
against RTF_CACHE, this means each of the three ->negative_advice()
existing methods must perform the sk_dst_reset() themselves.

Note the check against NULL dst is centralized in
__dst_negative_advice(), there is no need to duplicate
it in various callbacks.

Many thanks to Clement Lecigne for tracking this issue.

This old bug became visible after the blamed commit, using UDP sockets.

Bug: 343727534
Fixes: a87cb3e48ee8 ("net: Facility to report route quality of connected sockets")
Reported-by: Clement Lecigne <clecigne@google.com>
Diagnosed-by: Clement Lecigne <clecigne@google.com>
Signed-off-by: Eric Dumazet <edumazet@google.com>
Cc: Tom Herbert <tom@herbertland.com>
Reviewed-by: David Ahern <dsahern@kernel.org>
Link: https://lore.kernel.org/r/20240528114353.1794151-1-edumazet@google.com
Signed-off-by: Jakub Kicinski <kuba@kernel.org>
(cherry picked from commit 92f1655aa2b2294d0b49925f3b875a634bd3b59e)
[Lee: Trivial/unrelated conflict - no change to the patch]
Signed-off-by: Lee Jones <joneslee@google.com>
Change-Id: I293734dca1b81fcb712e1de294f51e96a405f7e4
[mkbestas: Non trivial backport to 4.14]
Signed-off-by: Michael Bestas <mkbestas@lineageos.org>
---
 include/net/dst_ops.h  |  2 +-
 include/net/sock.h     | 12 +++---------
 net/ipv4/route.c       | 22 ++++++++--------------
 net/ipv6/route.c       | 25 +++++++++++++------------
 net/xfrm/xfrm_policy.c | 11 +++--------
 5 files changed, 28 insertions(+), 44 deletions(-)

diff --git a/include/net/dst_ops.h b/include/net/dst_ops.h
index a0d443ca16fc..c3cd125032fa 100644
--- a/include/net/dst_ops.h
+++ b/include/net/dst_ops.h
@@ -23,7 +23,7 @@ struct dst_ops {
 	void			(*destroy)(struct dst_entry *);
 	void			(*ifdown)(struct dst_entry *,
 					  struct net_device *dev, int how);
-	struct dst_entry *	(*negative_advice)(struct dst_entry *);
+	void			(*negative_advice)(struct sock *sk, struct dst_entry *);
 	void			(*link_failure)(struct sk_buff *);
 	void			(*update_pmtu)(struct dst_entry *dst, struct sock *sk,
 					       struct sk_buff *skb, u32 mtu);
diff --git a/include/net/sock.h b/include/net/sock.h
index 8fe71ee1935a..8c29e159972e 100644
--- a/include/net/sock.h
+++ b/include/net/sock.h
@@ -1719,18 +1719,12 @@ sk_dst_get(struct sock *sk)

 static inline void dst_negative_advice(struct sock *sk)
 {
-	struct dst_entry *ndst, *dst = __sk_dst_get(sk);
+	struct dst_entry *dst = __sk_dst_get(sk);

 	sk_rethink_txhash(sk);

-	if (dst && dst->ops->negative_advice) {
-		ndst = dst->ops->negative_advice(dst);
-
-		if (ndst != dst) {
-			rcu_assign_pointer(sk->sk_dst_cache, ndst);
-			sk_tx_queue_clear(sk);
-		}
-	}
+	if (dst && dst->ops->negative_advice)
+		dst->ops->negative_advice(sk, dst);
 }

 static inline void
diff --git a/net/ipv4/route.c b/net/ipv4/route.c
index ec3d6750bbf1..18483e6c3897 100644
--- a/net/ipv4/route.c
+++ b/net/ipv4/route.c
@@ -138,7 +138,8 @@ static int ip_rt_gc_timeout __read_mostly	= RT_GC_TIMEOUT;
 static struct dst_entry *ipv4_dst_check(struct dst_entry *dst, u32 cookie);
 static unsigned int	 ipv4_default_advmss(const struct dst_entry *dst);
 static unsigned int	 ipv4_mtu(const struct dst_entry *dst);
-static struct dst_entry *ipv4_negative_advice(struct dst_entry *dst);
+static void		 ipv4_negative_advice(struct sock *sk,
+					   struct dst_entry *dst);
 static void		 ipv4_link_failure(struct sk_buff *skb);
 static void		 ip_rt_update_pmtu(struct dst_entry *dst, struct sock *sk,
 					   struct sk_buff *skb, u32 mtu);
@@ -821,22 +822,15 @@ static void ip_do_redirect(struct dst_entry *dst, struct sock *sk, struct sk_buf
 	__ip_do_redirect(rt, skb, &fl4, true);
 }

-static struct dst_entry *ipv4_negative_advice(struct dst_entry *dst)
+static void ipv4_negative_advice(struct sock *sk,
+				 struct dst_entry *dst)
 {
 	struct rtable *rt = (struct rtable *)dst;
-	struct dst_entry *ret = dst;

-	if (rt) {
-		if (dst->obsolete > 0) {
-			ip_rt_put(rt);
-			ret = NULL;
-		} else if ((rt->rt_flags & RTCF_REDIRECTED) ||
-			   rt->dst.expires) {
-			ip_rt_put(rt);
-			ret = NULL;
-		}
-	}
-	return ret;
+	if ((dst->obsolete > 0) ||
+	    (rt->rt_flags & RTCF_REDIRECTED) ||
+	    rt->dst.expires)
+		sk_dst_reset(sk);
 }

 /*
diff --git a/net/ipv6/route.c b/net/ipv6/route.c
index cf05b953f8b8..f841528ae658 100644
--- a/net/ipv6/route.c
+++ b/net/ipv6/route.c
@@ -81,7 +81,8 @@ static void ip6_rt_copy_init(struct rt6_info *rt, struct rt6_info *ort);
 static struct dst_entry	*ip6_dst_check(struct dst_entry *dst, u32 cookie);
 static unsigned int	 ip6_default_advmss(const struct dst_entry *dst);
 static unsigned int	 ip6_mtu(const struct dst_entry *dst);
-static struct dst_entry *ip6_negative_advice(struct dst_entry *);
+static void		ip6_negative_advice(struct sock *sk,
+					    struct dst_entry *dst);
 static void		ip6_dst_destroy(struct dst_entry *);
 static void		ip6_dst_ifdown(struct dst_entry *,
 				       struct net_device *dev, int how);
@@ -1311,22 +1312,22 @@ static struct dst_entry *ip6_dst_check(struct dst_entry *dst, u32 cookie)
 		return rt6_check(rt, cookie);
 }

-static struct dst_entry *ip6_negative_advice(struct dst_entry *dst)
+static void ip6_negative_advice(struct sock *sk,
+				struct dst_entry *dst)
 {
 	struct rt6_info *rt = (struct rt6_info *) dst;

-	if (rt) {
-		if (rt->rt6i_flags & RTF_CACHE) {
-			if (rt6_check_expired(rt)) {
-				ip6_del_rt(rt);
-				dst = NULL;
-			}
-		} else {
-			dst_release(dst);
-			dst = NULL;
+	if (rt->rt6i_flags & RTF_CACHE) {
+		if (rt6_check_expired(rt)) {
+			/* counteract the dst_release() in sk_dst_reset() */
+			dst_hold(dst);
+			sk_dst_reset(sk);
+
+			ip6_del_rt(rt);
 		}
+		return;
 	}
-	return dst;
+	sk_dst_reset(sk);
 }

 static void ip6_link_failure(struct sk_buff *skb)
diff --git a/net/xfrm/xfrm_policy.c b/net/xfrm/xfrm_policy.c
index e090ff476cdf..2a4f77b01936 100644
--- a/net/xfrm/xfrm_policy.c
+++ b/net/xfrm/xfrm_policy.c
@@ -2725,15 +2725,10 @@ static void xfrm_link_failure(struct sk_buff *skb)
 	/* Impossible. Such dst must be popped before reaches point of failure. */
 }

-static struct dst_entry *xfrm_negative_advice(struct dst_entry *dst)
+static void xfrm_negative_advice(struct sock *sk, struct dst_entry *dst)
 {
-	if (dst) {
-		if (dst->obsolete) {
-			dst_release(dst);
-			dst = NULL;
-		}
-	}
-	return dst;
+	if (dst->obsolete)
+		sk_dst_reset(sk);
 }

 void xfrm_garbage_collect(struct net *net)
--
2.34.1
0002-ANDROID-ABI-fixup-for-abi-break-in-struct-dst_ops.patch (4,965 bytes)
From 4d12c66b108d4c0cddc2948c9deeb5e3b0728b93 Mon Sep 17 00:00:00 2001
From: Greg Kroah-Hartman <gregkh@google.com>
Date: Sat, 1 Jun 2024 09:33:51 +0000
Subject: [PATCH 2/2] ANDROID: ABI fixup for abi break in struct dst_ops

In commit 92f1655aa2b2 ("net: fix __dst_negative_advice() race") the
struct dst_ops callback negative_advice is callback changes function
parameters.  But as this pointer is part of a structure that is tracked
in the ABI checker, the tool triggers when this is changed.

However, the callback pointer is internal to the networking stack, so
changing the function type is safe, so needing to preserve this is not
required.  To do so, switch the function pointer type back to the old
one so that the checking tools pass, AND then do a hard cast of the
function pointer to the new type when assigning and calling the
function.

Bug: 343727534
Fixes: 92f1655aa2b2 ("net: fix __dst_negative_advice() race")
Change-Id: I48d4ab4bbd29f8edc8fbd7923828b7f78a23e12e
Signed-off-by: Greg Kroah-Hartman <gregkh@google.com>
---
 include/net/dst_ops.h  | 12 +++++++++++-
 include/net/sock.h     | 12 ++++++++++--
 net/ipv4/route.c       |  2 +-
 net/ipv6/route.c       |  2 +-
 net/xfrm/xfrm_policy.c |  2 +-
 5 files changed, 24 insertions(+), 6 deletions(-)

diff --git a/include/net/dst_ops.h b/include/net/dst_ops.h
index c3cd125032fa..64e06d90c7a5 100644
--- a/include/net/dst_ops.h
+++ b/include/net/dst_ops.h
@@ -11,6 +11,16 @@ struct sk_buff;
 struct sock;
 struct net;

+/* *** ANDROID FIXUP ***
+ * These typedefs are used to help fixup the ABI break caused by commit
+ * 92f1655aa2b2 ("net: fix __dst_negative_advice() race") where the
+ * negative_advice callback changed function signatures.
+ * See b/343727534 for more details.
+ * *** ANDROID FIXUP ***
+ */
+typedef void (*android_dst_ops_negative_advice_new_t)(struct sock *sk, struct dst_entry *);
+typedef struct dst_entry * (*android_dst_ops_negative_advice_old_t)(struct dst_entry *);
+
 struct dst_ops {
 	unsigned short		family;
 	unsigned int		gc_thresh;
@@ -23,7 +33,7 @@ struct dst_ops {
 	void			(*destroy)(struct dst_entry *);
 	void			(*ifdown)(struct dst_entry *,
 					  struct net_device *dev, int how);
-	void			(*negative_advice)(struct sock *sk, struct dst_entry *);
+	struct dst_entry *	(*negative_advice)(struct dst_entry *);
 	void			(*link_failure)(struct sk_buff *);
 	void			(*update_pmtu)(struct dst_entry *dst, struct sock *sk,
 					       struct sk_buff *skb, u32 mtu);
diff --git a/include/net/sock.h b/include/net/sock.h
index 8c29e159972e..8a71f74e6bd9 100644
--- a/include/net/sock.h
+++ b/include/net/sock.h
@@ -1719,12 +1719,20 @@ sk_dst_get(struct sock *sk)

 static inline void dst_negative_advice(struct sock *sk)
 {
+	/* *** ANDROID FIXUP ***
+	 * See b/343727534 for more details why this typedef is needed here.
+	 * *** ANDROID FIXUP ***
+	 */
+	android_dst_ops_negative_advice_new_t negative_advice;
+
 	struct dst_entry *dst = __sk_dst_get(sk);

 	sk_rethink_txhash(sk);

-	if (dst && dst->ops->negative_advice)
-		dst->ops->negative_advice(sk, dst);
+	if (dst && dst->ops->negative_advice) {
+		negative_advice = (android_dst_ops_negative_advice_new_t)dst->ops->negative_advice;
+		negative_advice(sk, dst);
+	}
 }

 static inline void
diff --git a/net/ipv4/route.c b/net/ipv4/route.c
index 18483e6c3897..395108c7338e 100644
--- a/net/ipv4/route.c
+++ b/net/ipv4/route.c
@@ -164,7 +164,7 @@ static struct dst_ops ipv4_dst_ops = {
 	.mtu =			ipv4_mtu,
 	.cow_metrics =		ipv4_cow_metrics,
 	.destroy =		ipv4_dst_destroy,
-	.negative_advice =	ipv4_negative_advice,
+	.negative_advice =	(android_dst_ops_negative_advice_old_t)ipv4_negative_advice,
 	.link_failure =		ipv4_link_failure,
 	.update_pmtu =		ip_rt_update_pmtu,
 	.redirect =		ip_do_redirect,
diff --git a/net/ipv6/route.c b/net/ipv6/route.c
index f841528ae658..b6a31e83e1e3 100644
--- a/net/ipv6/route.c
+++ b/net/ipv6/route.c
@@ -228,7 +228,7 @@ static struct dst_ops ip6_dst_ops_template = {
 	.cow_metrics		=	ipv6_cow_metrics,
 	.destroy		=	ip6_dst_destroy,
 	.ifdown			=	ip6_dst_ifdown,
-	.negative_advice	=	ip6_negative_advice,
+	.negative_advice	=	(android_dst_ops_negative_advice_old_t)ip6_negative_advice,
 	.link_failure		=	ip6_link_failure,
 	.update_pmtu		=	ip6_rt_update_pmtu,
 	.redirect		=	rt6_do_redirect,
diff --git a/net/xfrm/xfrm_policy.c b/net/xfrm/xfrm_policy.c
index 2a4f77b01936..7855827323e5 100644
--- a/net/xfrm/xfrm_policy.c
+++ b/net/xfrm/xfrm_policy.c
@@ -2872,7 +2872,7 @@ int xfrm_policy_register_afinfo(struct xfrm_policy_afinfo *afinfo)
 		if (likely(dst_ops->mtu == NULL))
 			dst_ops->mtu = xfrm_mtu;
 		if (likely(dst_ops->negative_advice == NULL))
-			dst_ops->negative_advice = xfrm_negative_advice;
+			dst_ops->negative_advice = (android_dst_ops_negative_advice_old_t)xfrm_negative_advice;
 		if (likely(dst_ops->link_failure == NULL))
 			dst_ops->link_failure = xfrm_link_failure;
 		if (likely(dst_ops->neigh_lookup == NULL))
--
2.34.1
|
|
|
|
Hi Kinbay
I will check your suggestion by Monday and give you feedback.
Thank you
YK.Jung |
|
|
|
Hi Kinbay
There are a few things I want to check.
1) About patch date
>> The security vulnerability occurs after 0001-BACKPORT-net-fix-__dst_negative_advice-race.patch
>> Then fix by the 0002-ANDROID-ABI-fixup-for-abi-break-in-struct-dst_ops.patch.
0001-BACKPORT-net-fix-__dst_negative_advice-race.patch : Tue, 28 May 2024 11:43:53 +0000
0002-ANDROID-ABI-fixup-for-abi-break-in-struct-dst_ops.patch : Sat, 1 Jun 2024 09:33:51 +0000
Why is the resolved patch dated earlier?
2) Where did it say "0002-ANDROID-ABI-fixup-for-abi-break-in-struct-dst_ops.patch" was fixed?
How did you find it and share the link ?
3) fxn suggested ignoring it
If you know the difference between ignoring and applying two patches, please explain.
Other manufacturers are trying to apply it and will proceed with the test.
Thank you
YK.Jung |
|
|
|
Hi YK,
1) About patch date
=> I think it's correct to say 0001 comes before 0002.
2) Where did it say "0002-ANDROID-ABI-fixup-for-abi-break-in-struct-dst_ops.patch" was fixed?
=>
Sorry, I have a little ambiguous.
The two patches both fix the security vulnerability.
But the 0002 patch is true to correct the errors in the 0001 patch.
Please refer to the 0002 commit message for more details.
2-2) How did you find it and share the link?
=>
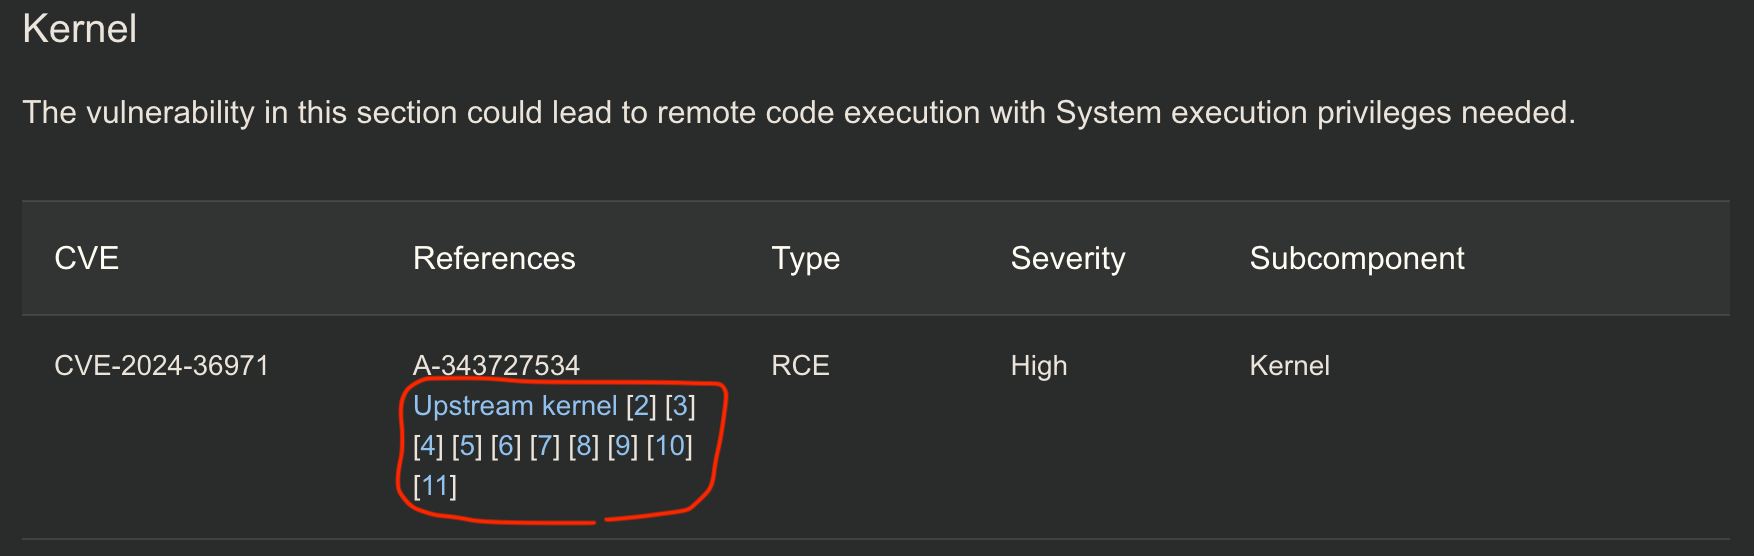
https://source.android.com/docs/security/bulletin/2024-08-01?authuser=1#Kernel
You can find it at Referneces (see attached screenshot).
And these 12 patches are duplicates. In fact, there are only two.
3) About fxn suggested ignoring it
=>
Because these two patches are modified based on the latest kernel
Our kernel has not been updated for a long time.
So we are worried that it will cause more problems after pushing two patches.
BR,
Kinbay |
|
|
|
Hi Kinbay
Thank you for update
Currently, other manufacturers, such as INTEK/INNOPIA, have different opinions on the patch.
I'll give you a feedback after we review together by next monday
and if I have any questions, I will ask you
Thank you
YK.Jung |
|
|
|
Hi Kinbay
I've discussed with other manufacturers (INTEK/INNOPIA), but there's no clear result yet.
However, other manufacturers are testing the patch first.
Anyway , It's described on the Google Security Bulletin.
https://source.android.com/docs/security/bulletin/2024-08-01?hl=ko
Can you ask 3PL if BFX-AT100 have to apply the patch or not?
Thank you
YK.Jung |
|
|
|
Hi YK
I asked the 3PL, and they indicated that the severity is high, so we must apply it.
BR,
Kinbay |
|
|
|
Hi Kinbay
I got it , then please apply the patchs and test it, so if there is no problem, please share them
Before you push the bitbucket , we are going to proceed with the stability test.
Thank you
YK.Jung |
|
|
|
Hi Kinbay
Please make a test branch with the patchs and let me know.
then we will test it
Thank you
YK.Jung |
|
|
|
Hi YK,
Our SQA team is helping with the testing.
Which branch should I base on? 543 / 542 / 542_CUG
BR,
Kinbay |
|
|
|
Hi Kinbay
Please use UI543 branch as the base.
Thank you
YK.Jung |
|
|
|
Hi YK,
I've pushed a new branch named [mantis1978].
Please check it.
BR,
Kinbay |
|
|
|
Hi Kinbay
OK , I checked mantis1978
Thank you
YK.Jung |
|
|
|
Hi KInbay
Please apply this patch to UI543
Thank you
YK.Jung |
|
|
|
Hi YK,
Merge done.
Please check it.
BR,
Kinbay |
|
|
|
Hi Kinbay
it's ok ,
I will close this ticket.
Thank you
YK.Jung |
|